
📦 GitHub 全球红队渗透资源中转站。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Docker #POC
📦 项目名称: bugxhunter-runner
👤 项目作者: cintelis
🛠 开发语言: TypeScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 12:02:51
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Docker #POC
📦 项目名称: bugxhunter-runner
👤 项目作者: cintelis
🛠 开发语言: TypeScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 12:02:51
📝 项目描述:
BugXHunter security-testing agent runner: web UI for the OpenCode agent on open-weight models via SCX, with per-action approvals and a sandboxed Docker agent🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #钓鱼 #Phishing
📦 项目名称: postmortem-phishing-response
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 11:24:13
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #钓鱼 #Phishing
📦 项目名称: postmortem-phishing-response
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 11:24:13
📝 项目描述:
复盘报告与钓鱼响应卡 — Post-Mortem 复盘报告生成 + 钓鱼事件三档分钟级处置卡。🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Exploit #CVE
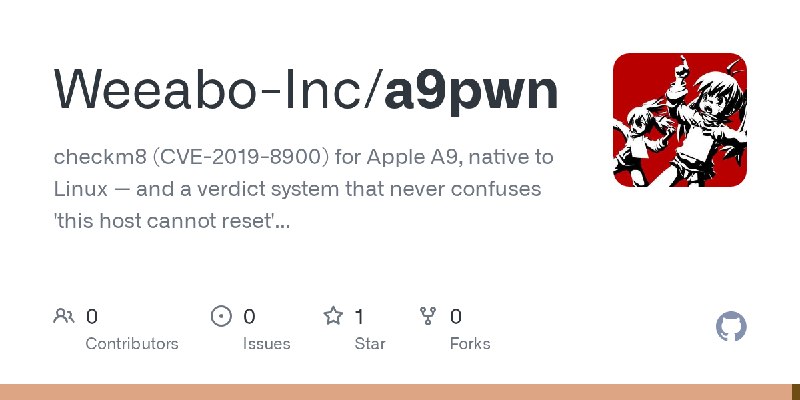
📦 项目名称: a9pwn
👤 项目作者: Weeabo-Inc
🛠 开发语言: Rust
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 10:46:16
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Exploit #CVE
📦 项目名称: a9pwn
👤 项目作者: Weeabo-Inc
🛠 开发语言: Rust
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 10:46:16
📝 项目描述:
checkm8 (CVE-2019-8900) for Apple A9, native to Linux — and a verdict system that never confuses 'this host cannot reset' with 'the exploit did not work'.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #0day #POC
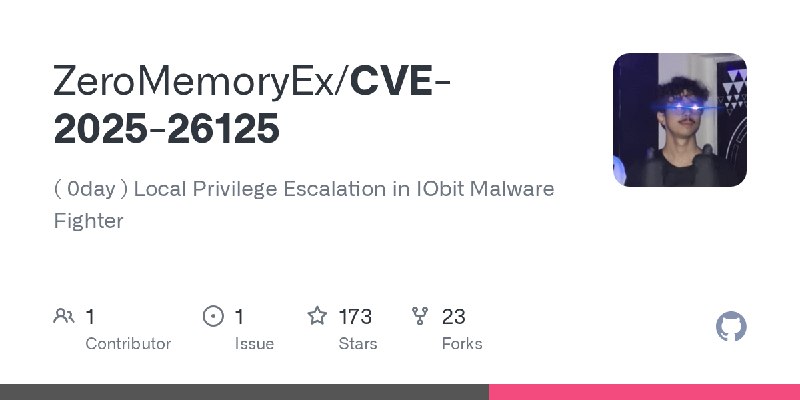
📦 项目名称: CVE-2025-26125
👤 项目作者: ZeroMemoryEx
🛠 开发语言: C
⭐ Star数量: 171 | 🍴 Fork数量: 22
📅 更新时间: 2026-10-07 10:43:47
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #0day #POC
📦 项目名称: CVE-2025-26125
👤 项目作者: ZeroMemoryEx
🛠 开发语言: C
⭐ Star数量: 171 | 🍴 Fork数量: 22
📅 更新时间: 2026-10-07 10:43:47
📝 项目描述:
( 0day ) Local Privilege Escalation in IObit Malware Fighter🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Reflected
📦 项目名称: DG_Interns_Hub_Week7_network_security
👤 项目作者: susmitha-17
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:59:23
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Reflected
📦 项目名称: DG_Interns_Hub_Week7_network_security
👤 项目作者: susmitha-17
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:59:23
📝 项目描述:
Performed web application reconnaissance, request interception, SQL Injection, Reflected XSS, authentication testing, parameter tampering, command injection, and endpoint discovery. Documented vulnerabilities, evidence, impacts, and recommended security measures.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Nuclei #templates #CVE
📦 项目名称: webenum-ng
👤 项目作者: zakeelm6
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 10:03:25
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Nuclei #templates #CVE
📦 项目名称: webenum-ng
👤 项目作者: zakeelm6
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 10:03:25
📝 项目描述:
All-in-one web recon orchestrator (the "enum4linux-ng of the web"): parallel fingerprint, content discovery, vuln scan and CMS tools, with product-aware nuclei and prioritized next-step recommendations.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #SSTI #POC
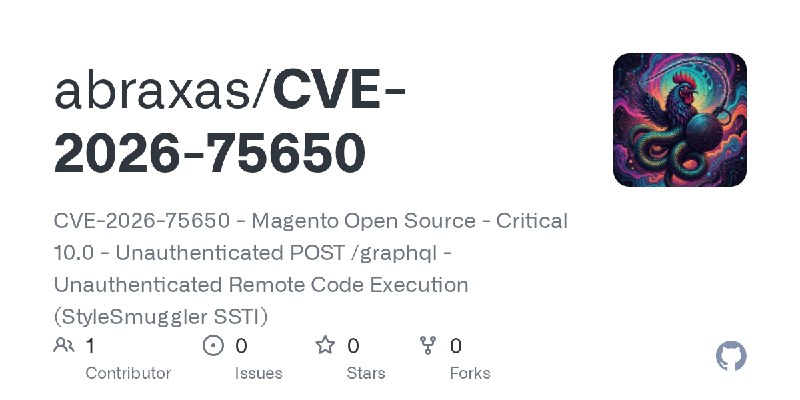
📦 项目名称: CVE-2026-75650
👤 项目作者: abraxas
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 01:06:53
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #SSTI #POC
📦 项目名称: CVE-2026-75650
👤 项目作者: abraxas
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 01:06:53
📝 项目描述:
CVE-2026-75650 - Magento Open Source - Critical 10.0 - Unauthenticated POST /graphql - Unauthenticated Remote Code Execution (StyleSmuggler SSTI)🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #SSTI #RCE
📦 项目名称: Do-Not-Disturb-TryHackMe-Walkthrough
👤 项目作者: anurag-rvnkr1
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:38:03
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #SSTI #RCE
📦 项目名称: Do-Not-Disturb-TryHackMe-Walkthrough
👤 项目作者: anurag-rvnkr1
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:38:03
📝 项目描述:
Professional walkthrough of the Do Not Disturb TryHackMe room, demonstrating web application exploitation through NoSQL Injection, Server-Side Template Injection, Remote Code Execution and Linux privilege escalation using debugfs and the disk group. Includes methodology, attack chain, screenshots, mitigations, and GitHub Pages documentation.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #信息收集 #渗透
📦 项目名称: security-scripts
👤 项目作者: mx4329144-oss
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:18:07
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #信息收集 #渗透
📦 项目名称: security-scripts
👤 项目作者: mx4329144-oss
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:18:07
📝 项目描述:
网络安全简易Python脚本,包含信息收集、靶场辅助工具🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #钓鱼 #二维码 #Phishing
📦 项目名称: phishing-url-qr-checker
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:24:37
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #钓鱼 #二维码 #Phishing
📦 项目名称: phishing-url-qr-checker
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:24:37
📝 项目描述:
钓鱼链接与二维码检测 — 12 项启发式特征静态分析可疑链接与二维码内容,全程不访问目标。🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #SQL注入 #漏洞
📦 项目名称: vuln-lab
👤 项目作者: mx4329144-oss
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:17:12
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #SQL注入 #漏洞
📦 项目名称: vuln-lab
👤 项目作者: mx4329144-oss
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:17:12
📝 项目描述:
Web漏洞复现学习笔记,包含SQL注入、XSS等漏洞原理与实操步骤🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #RCE
📦 项目名称: the-cookie-in-the-error-message-cve-2026-102489-zammad-session-hijack-to-rce
👤 项目作者: Hunt-Benito
🛠 开发语言: Ruby
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:56:01
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #RCE
📦 项目名称: the-cookie-in-the-error-message-cve-2026-102489-zammad-session-hijack-to-rce
👤 项目作者: Hunt-Benito
🛠 开发语言: Ruby
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 09:56:01
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #弱口令 #口令 #密码 #password
📦 项目名称: password-2fa-education
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:26:27
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #弱口令 #口令 #密码 #password
📦 项目名称: password-2fa-education
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:26:27
📝 项目描述:
弱密码与双因子教育 — 弱口令破解时间对照演示与 2FA 方案选型参谋,密码安全宣传配套。🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Reflected
📦 项目名称: SWYNEX-Web-Security-Review
👤 项目作者: thaila-m
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:57:45
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Reflected
📦 项目名称: SWYNEX-Web-Security-Review
👤 项目作者: thaila-m
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:57:45
📝 项目描述:
Defensive web security review of an authorized Metasploitable2/DVWA lab, covering service discovery, legacy web services, exposed applications, reflected XSS, evidence, severity, and remediation recommendations🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #钓鱼 #邮件 #Phishing
📦 项目名称: phishing-email-analyzer
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:25:04
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #钓鱼 #邮件 #Phishing
📦 项目名称: phishing-email-analyzer
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:25:04
📝 项目描述:
钓鱼邮件与邮件头分析 — 解析邮件原文与邮件头,识别域名伪造、认证失败与话术特征并量化可疑度。🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #钓鱼 #Phishing
📦 项目名称: phishing-awareness-quiz
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:25:59
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #钓鱼 #Phishing
📦 项目名称: phishing-awareness-quiz
👤 项目作者: sheyunyang
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:25:59
📝 项目描述:
钓鱼防范互动测验 — 10 道真实场景钓鱼识别题,即时判分讲解,适合全员安全意识考核。🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: Geekmonster
👤 项目作者: amboob223
🛠 开发语言: JavaScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 07:53:48
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: Geekmonster
👤 项目作者: amboob223
🛠 开发语言: JavaScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 07:53:48
📝 项目描述:
This is My Vulnerability scanner🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: web-vulnerability-scanner
👤 项目作者: bjoy8
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 07:59:45
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: web-vulnerability-scanner
👤 项目作者: bjoy8
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 07:59:45
📝 项目描述:
Non-destructive web vulnerability scanner built with Python and Flask, featuring CLI/web UI and HTML/PDF security reports.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Reflected #DOM
📦 项目名称: purify-edge
👤 项目作者: anzal1
🛠 开发语言: JavaScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:03:45
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Reflected #DOM
📦 项目名称: purify-edge
👤 项目作者: anzal1
🛠 开发语言: JavaScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 08:03:45
📝 项目描述:
DOMPurify without jsdom. Byte-identical output to DOMPurify on jsdom, about 65 KB gzipped, runs on Cloudflare Workers and other edge runtimes.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Nuclei #templates
📦 项目名称: Nuclei_Templates
👤 项目作者: msinabil14
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 06:55:26
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Nuclei #templates
📦 项目名称: Nuclei_Templates
👤 项目作者: msinabil14
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-07 06:55:26
📝 项目描述:
无描述🔗 点击访问项目地址
