
📦 GitHub 全球红队渗透资源中转站。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader #Evasion #EDR #AV
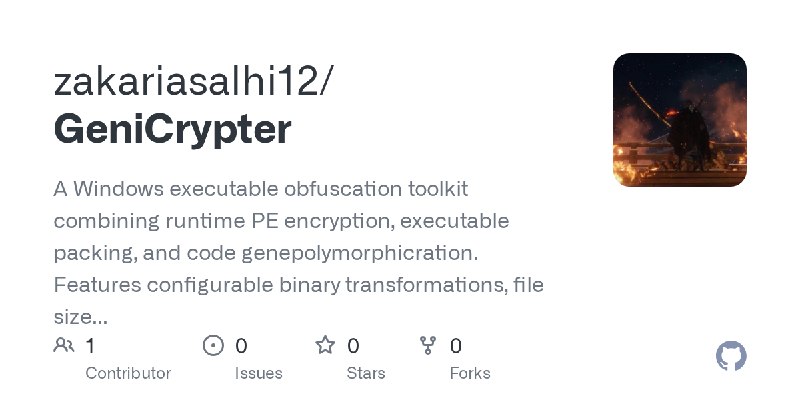
📦 项目名称: GeniCrypter
👤 项目作者: zakariasalhi12
🛠 开发语言: Rust
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-14 11:32:12
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader #Evasion #EDR #AV
📦 项目名称: GeniCrypter
👤 项目作者: zakariasalhi12
🛠 开发语言: Rust
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-14 11:32:12
📝 项目描述:
A Rust toolkit for Windows x64: an in-memory PE crypter (AES-256-GCM + zstd, manual mapping, anti-analysis, user-level persistence) and a polymorphic shellcode loader (indirect syscalls, ETW patching, self-mutating file signature)🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion #AV
📦 项目名称: WindowsStagingProject
👤 项目作者: jwfawcett
🛠 开发语言: C++
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-11 14:49:24
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion #AV
📦 项目名称: WindowsStagingProject
👤 项目作者: jwfawcett
🛠 开发语言: C++
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-11 14:49:24
📝 项目描述:
An example of web based staging for shellcode, also contains basic AV evasion🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: Polymorphic-Shellcode-Engine
👤 项目作者: Aviral2642
🛠 开发语言: Python
⭐ Star数量: 5 | 🍴 Fork数量: 1
📅 更新时间: 2026-11-09 05:44:30
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: Polymorphic-Shellcode-Engine
👤 项目作者: Aviral2642
🛠 开发语言: Python
⭐ Star数量: 5 | 🍴 Fork数量: 1
📅 更新时间: 2026-11-09 05:44:30
📝 项目描述:
A next-generation engine for generating metamorphic shellcode payloads with built-in evasion capabilities, designed for red team operations and penetration testing.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader #Execute #Evasion #EDR #AV
📦 项目名称: Alma_evader
👤 项目作者: Almavj
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-04 21:14:03
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader #Execute #Evasion #EDR #AV
📦 项目名称: Alma_evader
👤 项目作者: Almavj
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-04 21:14:03
📝 项目描述:
Alma Evader takes raw shellcode (from any C2 framework) and produces a fully self-contained Windows DLL or EXE🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader #Evasion
📦 项目名称: Winx86_64-Encoded-Shellcode-Loader
👤 项目作者: aghaasfandyarkhan
🛠 开发语言: Rust
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-04 13:58:56
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader #Evasion
📦 项目名称: Winx86_64-Encoded-Shellcode-Loader
👤 项目作者: aghaasfandyarkhan
🛠 开发语言: Rust
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-04 13:58:56
📝 项目描述:
This is the another version of Shellcode Loader where I encoded the URL using XOR single byte and it mostly performs signature based evasion and sometimes Full Windows Antivirus Evasion too.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Execute #Evasion
📦 项目名称: Cybersecurity-CTF-Labs-Collection-Exploit-Development-Reverse-Engineering
👤 项目作者: sifatnotes
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-03 05:55:38
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Execute #Evasion
📦 项目名称: Cybersecurity-CTF-Labs-Collection-Exploit-Development-Reverse-Engineering
👤 项目作者: sifatnotes
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-03 05:55:38
📝 项目描述:
A curated, searchable index of hands-on CTF labs covering binary mitigations, stack overflows, ROP chain construction, heap exploitation, format string bugs, shellcode development, and malware reverse engineering from Learn SecByte.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: Position_Independent_Backdoor
👤 项目作者: shaddy43
🛠 开发语言: Assembly
⭐ Star数量: 7 | 🍴 Fork数量: 2
📅 更新时间: 2026-10-31 10:13:33
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: Position_Independent_Backdoor
👤 项目作者: shaddy43
🛠 开发语言: Assembly
⭐ Star数量: 7 | 🍴 Fork数量: 2
📅 更新时间: 2026-10-31 10:13:33
📝 项目描述:
Complete methodology of creating custom shellcodes for injection and evasion🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader #Inject #Execute #Evasion #EDR #AV
📦 项目名称: lilith
👤 项目作者: anatemnein
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 17:48:27
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader #Inject #Execute #Evasion #EDR #AV
📦 项目名称: lilith
👤 项目作者: anatemnein
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 17:48:27
📝 项目描述:
Polymorphic AMSI and shellcode bypass🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader #Inject #Evasion
📦 项目名称: ghidra-tools
👤 项目作者: Ekco-S64QTN6
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-24 18:14:59
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader #Inject #Evasion
📦 项目名称: ghidra-tools
👤 项目作者: Ekco-S64QTN6
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-24 18:14:59
📝 项目描述:
A headless Ghidra binary triage pipeline. Drop a binary and get a scored threat report in seven formats (TXT/JSON/MD/HTML/SARIF/YARA/MISP) — featuring ATT&CK-tagged imports, entropy analysis, shellcode detection, P-code emulation for string deobfuscation, and priority-ranked decompilation.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Inject #Execute #Evasion
📦 项目名称: SeDebugPrivilege-BOF
👤 项目作者: retimax
🛠 开发语言: C
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-24 00:45:19
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Inject #Execute #Evasion
📦 项目名称: SeDebugPrivilege-BOF
👤 项目作者: retimax
🛠 开发语言: C
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-24 00:45:19
📝 项目描述:
BOF that enables SeDebugPrivilege on the current process and injects shellcode into a target process. Designed for AdaptixC2. Not OpSec safe by default.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader #Evasion #EDR
📦 项目名称: EDR-Evasion-Shellcode-Exe-DLL-
👤 项目作者: Goodworkid0
🛠 开发语言: C++
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-22 14:09:04
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader #Evasion #EDR
📦 项目名称: EDR-Evasion-Shellcode-Exe-DLL-
👤 项目作者: Goodworkid0
🛠 开发语言: C++
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-22 14:09:04
📝 项目描述:
Windows shellcode-loader proof of concept for security research.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader #Evasion #EDR
📦 项目名称: rpocket-Shellcode-Memory-Fluctuation
👤 项目作者: forkhelpburn
🛠 开发语言: Unknown
⭐ Star数量: 29 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-20 15:03:46
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader #Evasion #EDR
📦 项目名称: rpocket-Shellcode-Memory-Fluctuation
👤 项目作者: forkhelpburn
🛠 开发语言: Unknown
⭐ Star数量: 29 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-20 15:03:46
📝 项目描述:
Advanced memory evasion PoC that cyclically encrypts shellcode and fluctuates between RW/NoAccess and RX memory protections to bypass memory scanners like Moneta and PE-Sieve. 🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: Malware-Analysis
👤 项目作者: AndreLanza1
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 14:54:47
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: Malware-Analysis
👤 项目作者: AndreLanza1
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 14:54:47
📝 项目描述:
Comprehensive static and dynamic analysis of a 32-bit Windows malware. Features MPRESS unpacking, API hashing evasion, shellcode injection, and C2 protocol reverse engineering.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion #AV
📦 项目名称: AV-Bypasser
👤 项目作者: 0Lunar
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-16 11:05:42
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion #AV
📦 项目名称: AV-Bypasser
👤 项目作者: 0Lunar
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-16 11:05:42
📝 项目描述:
A purely educational AV evasion tool for POSIX, featuring AES-encrypted shellcode and runtime memory injection.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: shellcode_evasion_framework
👤 项目作者: doantien-cyber
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-16 04:54:34
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: shellcode_evasion_framework
👤 项目作者: doantien-cyber
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-16 04:54:34
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: shellcode_evasion_framework
👤 项目作者: DoanTien09
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-15 20:06:54
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: shellcode_evasion_framework
👤 项目作者: DoanTien09
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-15 20:06:54
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion #AV
📦 项目名称: Metamorpheus
👤 项目作者: GB102
🛠 开发语言: Python
⭐ Star数量: 4 | 🍴 Fork数量: 1
📅 更新时间: 2026-10-13 13:33:45
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion #AV
📦 项目名称: Metamorpheus
👤 项目作者: GB102
🛠 开发语言: Python
⭐ Star数量: 4 | 🍴 Fork数量: 1
📅 更新时间: 2026-10-13 13:33:45
📝 项目描述:
A metamorphic shellcode obfuscator capable of generating more unique shellcodes than there are atoms in the OBSERVABLE UNIVERSE and designed for shellcodes/implants that need to run in W^X memory.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion
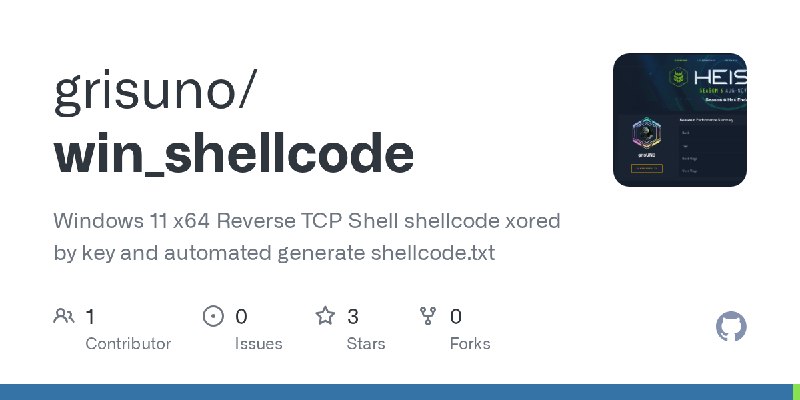
📦 项目名称: win_shellcode
👤 项目作者: grisuno
🛠 开发语言: Python
⭐ Star数量: 3 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-08 15:45:02
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion
📦 项目名称: win_shellcode
👤 项目作者: grisuno
🛠 开发语言: Python
⭐ Star数量: 3 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-08 15:45:02
📝 项目描述:
Windows 11 x64 Reverse TCP Shell shellcode xored by key and automated generate shellcode.txt🔗 点击访问项目地址