
📦 GitHub 全球红队渗透资源中转站。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Nuclei #templates
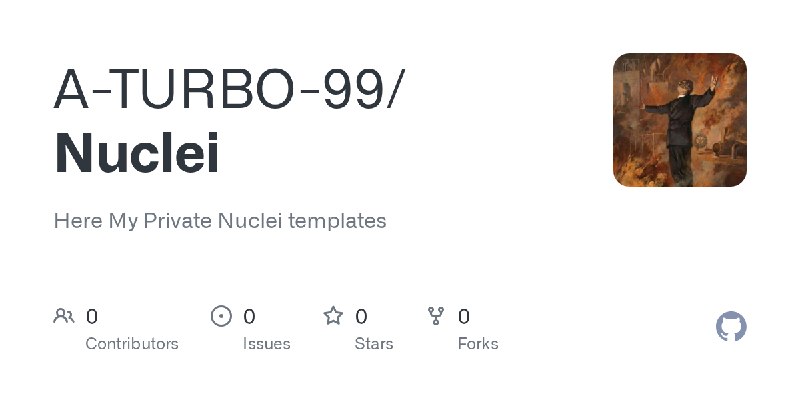
📦 项目名称: Nuclei
👤 项目作者: A-TURBO-99
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 20:55:20
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Nuclei #templates
📦 项目名称: Nuclei
👤 项目作者: A-TURBO-99
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 20:55:20
📝 项目描述:
Here My Private Nuclei templates🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #RCE
📦 项目名称: CVE-2026-110264
👤 项目作者: al4n4n
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 20:07:09
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #RCE
📦 项目名称: CVE-2026-110264
👤 项目作者: al4n4n
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 20:07:09
📝 项目描述:
CVE-2026-110264: GitLab pre-auth RCE via Onigmo integer overflow in org-ruby. Docker-based validation, admin check script, attack surface analysis.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: VScan
👤 项目作者: swaggpi
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:44:32
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: VScan
👤 项目作者: swaggpi
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:44:32
📝 项目描述:
Reachability-aware dependency vulnerability scanner🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
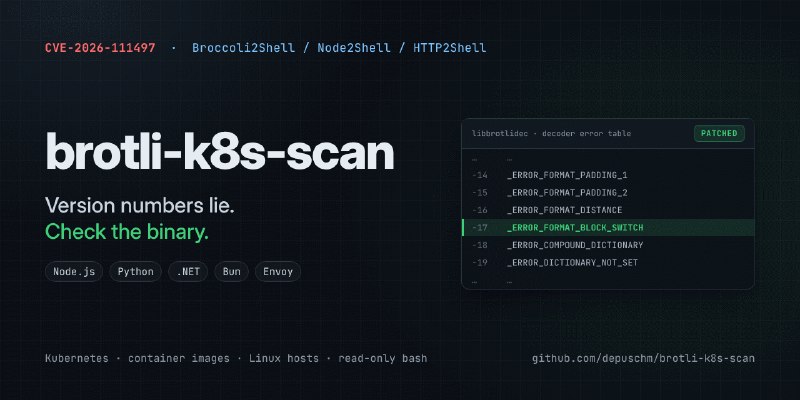
🚨 发现关键词: #YARA #rules
📦 项目名称: brotli-k8s-scan
👤 项目作者: depuschm
🛠 开发语言: Shell
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 20:00:43
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #YARA #rules
📦 项目名称: brotli-k8s-scan
👤 项目作者: depuschm
🛠 开发语言: Shell
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 20:00:43
📝 项目描述:
Find vulnerable Brotli (CVE-2026-111497, Broccoli2Shell / Node2Shell / HTTP2Shell) in Kubernetes clusters, container images and Linux hosts. Checks the binaries themselves, not just version numbers, so it catches bundled copies in Node.js, Python, .NET, Bun and Envoy. Read-only, bash only.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Exploit #POC
📦 项目名称: RainLab-User-Open-Redirect
👤 项目作者: 0p5cur
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:55:54
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Exploit #POC
📦 项目名称: RainLab-User-Open-Redirect
👤 项目作者: 0p5cur
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:55:54
📝 项目描述:
Open Redirect (CWE-601) in RainLab User Plugin for October CMS - PoC and exploit scripts🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader
📦 项目名称: Shellcode-Loader
👤 项目作者: 0xpainauwifi
🛠 开发语言: C
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:47:07
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader
📦 项目名称: Shellcode-Loader
👤 项目作者: 0xpainauwifi
🛠 开发语言: C
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:47:07
📝 项目描述:
A personal project for educational purposes🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Stored
📦 项目名称: safemedia
👤 项目作者: SimplepageUK
🛠 开发语言: C#
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:45:51
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Stored
📦 项目名称: safemedia
👤 项目作者: SimplepageUK
🛠 开发语言: C#
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:45:51
📝 项目描述:
Refuses unsafe SVG uploads in Umbraco before they are stored. MIT.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-5053
👤 项目作者: do4choo
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:57:00
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-5053
👤 项目作者: do4choo
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 19:57:00
📝 项目描述:
CVE-2026-5053: Writeup + PoC🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #免杀 #对抗
📦 项目名称: g_apk
👤 项目作者: 1252015115
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 16:23:40
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #免杀 #对抗
📦 项目名称: g_apk
👤 项目作者: 1252015115
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 16:23:40
📝 项目描述:
APK免杀 · 高频 · 去毒 · 保护,一体化处理🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Loader #Inject #Execute #Evasion #EDR #AV
📦 项目名称: lilith
👤 项目作者: anatemnein
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 17:48:27
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Loader #Inject #Execute #Evasion #EDR #AV
📦 项目名称: lilith
👤 项目作者: anatemnein
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 17:48:27
📝 项目描述:
Polymorphic AMSI and shellcode bypass🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Reflected
📦 项目名称: reflected_xss
👤 项目作者: anjanshivareddy
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 18:59:11
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Reflected
📦 项目名称: reflected_xss
👤 项目作者: anjanshivareddy
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 18:59:11
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #RCE #CVE #POC
📦 项目名称: CVE-2026-102785
👤 项目作者: al4n4n
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 18:49:31
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #RCE #CVE #POC
📦 项目名称: CVE-2026-102785
👤 项目作者: al4n4n
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 18:49:31
📝 项目描述:
CVE-2026-102785: YOOtheme Pro 5.0.0-5.0.52 unauthenticated RCE via image handler signature reuse + path traversal + JPEG/PHP polyglot. CVSS 10.0. Check script, exploit, detection rules.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #0day #Exploit
📦 项目名称: Jelly-Auto-Exploit
👤 项目作者: antid00t
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 17:24:48
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #0day #Exploit
📦 项目名称: Jelly-Auto-Exploit
👤 项目作者: antid00t
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 17:24:48
📝 项目描述:
Jelly Project, Jelly Auto Exploit, Wordpress Auto Exploit, Joomla Auto Exploit, Auto Webshell, Auto Shell Mass Tool, Shell Mass Tool🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #Exploit
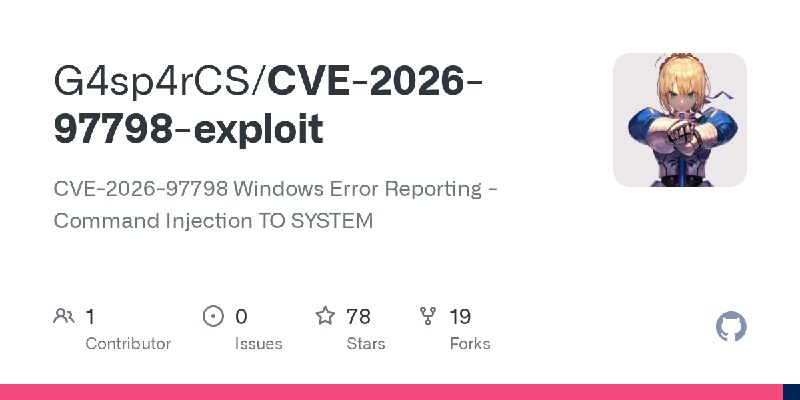
📦 项目名称: CVE-2026-97798-exploit
👤 项目作者: G4sp4rCS
🛠 开发语言: C++
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 17:59:41
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #Exploit
📦 项目名称: CVE-2026-97798-exploit
👤 项目作者: G4sp4rCS
🛠 开发语言: C++
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-27 17:59:41
📝 项目描述:
CVE-2026-97798 Windows Error Reporting - Command Injection TO SYSTEM🔗 点击访问项目地址