
📦 GitHub 全球红队渗透资源中转站。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-39987-PoC
👤 项目作者: stapat1245
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 20:10:36
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-39987-PoC
👤 项目作者: stapat1245
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 20:10:36
📝 项目描述:
CVE-2026-39987 Proof of Concept🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #C2 #Command and Control
📦 项目名称: pcap-analyzer
👤 项目作者: HunterBFranklin
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 19:58:27
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #C2 #Command and Control
📦 项目名称: pcap-analyzer
👤 项目作者: HunterBFranklin
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 19:58:27
📝 项目描述:
A behavioral network analysis tool that detects Command and Control (C2) beaconing, DNS anomalies, and known malicious infrastructure in live or captured traffic.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
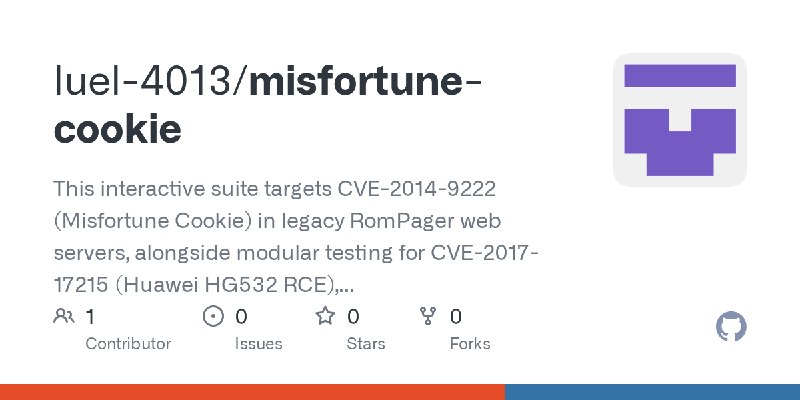
🚨 发现关键词: #Exploit #CVE #RCE
📦 项目名称: misfortune-cookie
👤 项目作者: luel-4013
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 19:59:01
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Exploit #CVE #RCE
📦 项目名称: misfortune-cookie
👤 项目作者: luel-4013
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 19:59:01
📝 项目描述:
This interactive suite targets CVE-2014-9222 (Misfortune Cookie) in legacy RomPager web servers, alongside modular testing for CVE-2017-17215 (Huawei HG532 RCE), CVE-2018-14847 (MikroTik WinBox credential leak), and the CVE-2021-27101 / CVE-2021-27102 exploit chain (Accellion FTA).🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Burp #Extension
📦 项目名称: prub
👤 项目作者: parsiya
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 19:47:49
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Burp #Extension
📦 项目名称: prub
👤 项目作者: parsiya
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 19:47:49
📝 项目描述:
Reverse engineering the Burp project format to create a extractor tool.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Shellcode #Evasion #EDR
📦 项目名称: Windows-Process-Injector-C
👤 项目作者: Michel-DV
🛠 开发语言: C
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 18:19:34
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Shellcode #Evasion #EDR
📦 项目名称: Windows-Process-Injector-C
👤 项目作者: Michel-DV
🛠 开发语言: C
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 18:19:34
📝 项目描述:
Shellcode Injection using WinAPI. Educational research on memory manipulation and EDR evasion techniques.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Log4j #CVE
📦 项目名称: transdep-demo-util-common
👤 项目作者: siddharthoak
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 10:32:24
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Log4j #CVE
📦 项目名称: transdep-demo-util-common
👤 项目作者: siddharthoak
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 10:32:24
📝 项目描述:
Demo: company-standard logging/tracing util lib. Part of a 3-repo chain used to test transitive-dependency vulnerability handling in vuln-remediation-agent. Deliberately depends on a vulnerable log4j-core version.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Credential Dumping #Mimikatz
📦 项目名称: Active-Directory-Penetration-Testing-Lab
👤 项目作者: franklinlatouche
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 18:57:21
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Credential Dumping #Mimikatz
📦 项目名称: Active-Directory-Penetration-Testing-Lab
👤 项目作者: franklinlatouche
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 18:57:21
📝 项目描述:
Full build-and-attack writeup for a self-hosted AD lab: domain controller setup, realistic domain population, then a full attack chain against it, SMB/LDAP enumeration, Kerberoasting and ASREPRoasting with Impacket, BloodHound-driven privilege escalation mapping, and credential dumping.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-32247
👤 项目作者: romain-deperne
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:20
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-32247
👤 项目作者: romain-deperne
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:20
📝 项目描述:
Cypher injection in Graphiti via unsanitized node_labels — CVE-2026-32247 / CVSS 8.1🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #YARA #rules #malware
📦 项目名称: PackClient
👤 项目作者: ivanimmanuel-dev
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:57:28
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #YARA #rules #malware
📦 项目名称: PackClient
👤 项目作者: ivanimmanuel-dev
🛠 开发语言: Python
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:57:28
📝 项目描述:
Reverse engineering and runtime analysis of the PackClient modular RAT framework, including protocol reconstruction, tooling, detections, and reproducible evidence.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Confluence #CVE
📦 项目名称: CVE-2026-77262
👤 项目作者: romain-deperne
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:19
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Confluence #CVE
📦 项目名称: CVE-2026-77262
👤 项目作者: romain-deperne
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:19
📝 项目描述:
Arbitrary file read in mcp-atlassian via confluence_upload_attachment — CVE-2026-77262 / GHSA-p6hp-93wp-fh6p🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Burp #Extension
📦 项目名称: zap-ghostjs
👤 项目作者: ArkhaMahn
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:45:58
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Burp #Extension
📦 项目名称: zap-ghostjs
👤 项目作者: ArkhaMahn
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:45:58
📝 项目描述:
GhostJS — ZAP add-on that passively scans JavaScript responses for hard-coded secrets and discovers API endpoints, source maps, and cloud-storage URLs (port of Ghost-Js-Burp-Extension).🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: android-application-penetration-testing
👤 项目作者: sravanibandreddy
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:48:25
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: android-application-penetration-testing
👤 项目作者: sravanibandreddy
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:48:25
📝 项目描述:
Android Security Assessment and SAST Vulnerability Scanner based on OWASP MASVS & Mobile Top 5🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #RCE #CVE
📦 项目名称: cpanel-whm-authbypass-to-rce
👤 项目作者: bright77777
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 16:45:59
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #RCE #CVE
📦 项目名称: cpanel-whm-authbypass-to-rce
👤 项目作者: bright77777
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 16:45:59
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #SSRF #POC
📦 项目名称: week-4-websec-w01-advanced
👤 项目作者: itsmariamfatima
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:27:23
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #SSRF #POC
📦 项目名称: week-4-websec-w01-advanced
👤 项目作者: itsmariamfatima
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:27:23
📝 项目描述:
PortSwigger Web Security Academy — Advanced Track. Hands-on exploitation of SSRF, Insecure Deserialization, and SSTI, with full PDF report and PoC screenshots.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #SSRF #CVE
📦 项目名称: CVE-2026-33715
👤 项目作者: romain-deperne
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:21
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #SSRF #CVE
📦 项目名称: CVE-2026-33715
👤 项目作者: romain-deperne
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:21
📝 项目描述:
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-34940
👤 项目作者: romain-deperne
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:25
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-34940
👤 项目作者: romain-deperne
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:25
📝 项目描述:
OS command injection in KubeAI via an Ollama model URL — CVE-2026-34940 / CVSS 8.7🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-34975
👤 项目作者: romain-deperne
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:26
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #POC
📦 项目名称: CVE-2026-34975
👤 项目作者: romain-deperne
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 17:44:26
📝 项目描述:
CRLF email header injection in Plunk raw MIME construction — CVE-2026-34975 / CVSS 8.5🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Stored
📦 项目名称: bifrost-xss-disclosure
👤 项目作者: ChristopherPatrickKuntz
🛠 开发语言: Shell
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 16:24:08
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Stored
📦 项目名称: bifrost-xss-disclosure
👤 项目作者: ChristopherPatrickKuntz
🛠 开发语言: Shell
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 16:24:08
📝 项目描述:
Bifrost Finance — stored XSS via backend database leading to one-click wallet drain. Submitted via Immunefi.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Log4j #CVE
📦 项目名称: transdep-demo-app
👤 项目作者: siddharthoak
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 10:33:18
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Log4j #CVE
📦 项目名称: transdep-demo-app
👤 项目作者: siddharthoak
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 10:33:18
📝 项目描述:
Demo: leaf app depending on transdep-demo-service-lib (2 hops from a vulnerable log4j-core dep in transdep-demo-util-common). Test target for the transitive-dependency gap in vuln-remediation-agent.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Log4j #CVE
📦 项目名称: m5-log4shell-demo
👤 项目作者: aureliusgovenai
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 14:19:29
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Log4j #CVE
📦 项目名称: m5-log4shell-demo
👤 项目作者: aureliusgovenai
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-09-07 14:19:29
📝 项目描述:
Aurelius M5 demo — Maven project with a deliberately outdated log4j-core for the log4shell-bump patch runner to fix🔗 点击访问项目地址
