
📦 GitHub 全球红队渗透资源中转站。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Stored
📦 项目名称: PHP-Shield
👤 项目作者: paulmann
🛠 开发语言: PHP
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 21:52:13
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Stored
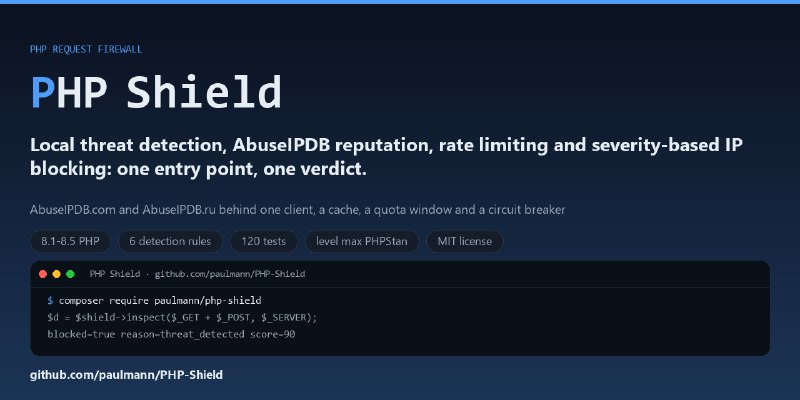
📦 项目名称: PHP-Shield
👤 项目作者: paulmann
🛠 开发语言: PHP
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 21:52:13
📝 项目描述:
Modular PHP request firewall: SQLi/XSS/traversal detection, AbuseIPDB.com and .ru reputation, rate limiting, severity-based IP blocks, incident journal, admin dashboard.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Burp #Extension
📦 项目名称: PHP-Payload-Editor
👤 项目作者: tobiasGuta
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 22:05:01
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Burp #Extension
📦 项目名称: PHP-Payload-Editor
👤 项目作者: tobiasGuta
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 22:05:01
📝 项目描述:
A Burp Suite extension that adds a dedicated PHP code editor to Repeater, featuring syntax highlighting, automatic PHP detection, and seamless editing of PHP payloads within HTTP requests, including multipart file uploads.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #YARA #malware
📦 项目名称: olivebloom-githook-dropper-analysis
👤 项目作者: jafeeri
🛠 开发语言: PowerShell
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 21:48:45
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #YARA #malware
📦 项目名称: olivebloom-githook-dropper-analysis
👤 项目作者: jafeeri
🛠 开发语言: PowerShell
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 21:48:45
📝 项目描述:
Analysis of a git post-checkout hook dropper delivered via a fake freelance client: social-engineering lure, static triage, infrastructure intelligence, host assessment, and controlled detonation🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #C2 #Framework
📦 项目名称: ExploitPeek
👤 项目作者: digitizables
🛠 开发语言: C#
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 22:00:38
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #C2 #Framework
📦 项目名称: ExploitPeek
👤 项目作者: digitizables
🛠 开发语言: C#
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 22:00:38
📝 项目描述:
Native Windows RE workbench: PE scan, findings triage, reverse/debug/diff shells, and an optional lab C2 channel. Remake of 0xwarl0ck/ExploitPeek.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #YARA #rules
📦 项目名称: detections-public
👤 项目作者: Medina-Telemetry-Systems
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 21:06:38
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #YARA #rules
📦 项目名称: detections-public
👤 项目作者: Medina-Telemetry-Systems
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 21:06:38
📝 项目描述:
Free sample detection rules and advisories from Medina Telemetry Systems🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Exploit #CVE
📦 项目名称: securityexplorer
👤 项目作者: MinoCodi
🛠 开发语言: TypeScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 20:49:49
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Exploit #CVE
📦 项目名称: securityexplorer
👤 项目作者: MinoCodi
🛠 开发语言: TypeScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 20:49:49
📝 项目描述:
Interactive 3D cybersecurity, CVE exploit & patched defense architecture simulator — step-by-step packet visualizer, hex inspector & live threat lab.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #RCE #CVE #POC #Remote Code Execution
📦 项目名称: CVE-2023-34468-Apache-NiFi-RCE
👤 项目作者: mohammed-moshii
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 21:02:16
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #RCE #CVE #POC #Remote Code Execution
📦 项目名称: CVE-2023-34468-Apache-NiFi-RCE
👤 项目作者: mohammed-moshii
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 21:02:16
📝 项目描述:
CVE-2023-34468: Apache NiFi 1.21.0 Remote Code Execution (ExecuteProcess Variant) - Security Research & Analysis by Mohammed Moshii🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #越权 #漏洞
📦 项目名称: ai-security-guard
👤 项目作者: xscanzm
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 14:57:27
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #越权 #漏洞
📦 项目名称: ai-security-guard
👤 项目作者: xscanzm
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 14:57:27
📝 项目描述:
给 AI 项目装一句默认的安全咒语:代码后门、Skill 越权、文档隐私、文件夹权限,四域本地体检。🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: VulnScan
👤 项目作者: vixi-max
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 19:19:08
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: VulnScan
👤 项目作者: vixi-max
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 19:19:08
📝 项目描述:
Educational web vulnerability scanner built with Python and Flask🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: lh-visitor-audit
👤 项目作者: Logihertz-Systems-OPC-Pvt-Ltd
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 19:45:56
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: lh-visitor-audit
👤 项目作者: Logihertz-Systems-OPC-Pvt-Ltd
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 19:45:56
📝 项目描述:
Analyzes HTTP access logs (Combined/JSON/CloudFront/Cloudflare) to detect directory brute-forcing, vulnerability scanner fingerprints (Nuclei/Nikto/SQLMap), credential stuffing bursts, and anomalous L7 scraping velocity.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Exploit #CVE #POC
📦 项目名称: salt-cve-2020-11651-poc
👤 项目作者: codenamepetrel
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 19:56:37
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Exploit #CVE #POC
📦 项目名称: salt-cve-2020-11651-poc
👤 项目作者: codenamepetrel
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 19:56:37
📝 项目描述:
Dependency-free PoC for SaltStack CVE-2020-11651/11652 that runs on modern Python (pyzmq + msgpack, no salt library)🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #RCE #POC
📦 项目名称: openhands-sdk-unauthenticated-rce
👤 项目作者: ZSH402
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 17:04:42
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #RCE #POC
📦 项目名称: openhands-sdk-unauthenticated-rce
👤 项目作者: ZSH402
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 17:04:42
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #RCE #CVE
📦 项目名称: CVE_2021-41773_ApachePathTraversal_RCE
👤 项目作者: sheema-ruzaik
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 18:39:13
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #RCE #CVE
📦 项目名称: CVE_2021-41773_ApachePathTraversal_RCE
👤 项目作者: sheema-ruzaik
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 18:39:13
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #RCE #POC
📦 项目名称: surveyproject-filemanager-advisory
👤 项目作者: einsteinstein
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 18:07:32
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #RCE #POC
📦 项目名称: surveyproject-filemanager-advisory
👤 项目作者: einsteinstein
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 18:07:32
📝 项目描述:
Security advisory and PoC: unauthenticated file upload, file read and RCE in the Survey Project (NSurvey) Filemanager ASP.NET connector🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Burp #Extension
📦 项目名称: UploadHunt
👤 项目作者: tobiasGuta
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 17:51:24
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Burp #Extension
📦 项目名称: UploadHunt
👤 项目作者: tobiasGuta
🛠 开发语言: Java
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 17:51:24
📝 项目描述:
UploadHunt is a Burp Suite extension designed to help security researchers and bug bounty hunters identify potential file-upload vulnerabilities. Using a rule-based hypothesis engine.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Burp #Extension
📦 项目名称: PhoenixBox
👤 项目作者: avihayf
🛠 开发语言: JavaScript
⭐ Star数量: 5 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 18:01:36
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Burp #Extension
📦 项目名称: PhoenixBox
👤 项目作者: avihayf
🛠 开发语言: JavaScript
⭐ Star数量: 5 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 18:01:36
📝 项目描述:
Firefox containers for security testing and bug bounty hunting, with isolated sessions, per-container proxies, User-Agent overrides, and Burp Suite integration through dedicated proxy listeners.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Stored #Reflected #DOM
📦 项目名称: lh-payload-guard
👤 项目作者: Logihertz-Systems-OPC-Pvt-Ltd
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 17:30:03
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Stored #Reflected #DOM
📦 项目名称: lh-payload-guard
👤 项目作者: Logihertz-Systems-OPC-Pvt-Ltd
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-11-07 17:30:03
📝 项目描述:
HTTP request payload inspector for SQLi, XSS, SSTI, and path traversal🔗 点击访问项目地址