
📦 GitHub 全球红队渗透资源中转站。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
旨在收录那些“好用却难找”的安全项目。
🔗 定时推送:GitHub Trending (Security)
🛠 必备清单:后渗透、远控、免杀、提权工具集
📅 更新频率:每日精选,绝不灌水。
⚠️ 本频道仅供安全研究与授权测试使用。
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: stackradar
👤 项目作者: lockdep
🛠 开发语言: TypeScript
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 13:47:23
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: stackradar
👤 项目作者: lockdep
🛠 开发语言: TypeScript
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 13:47:23
📝 项目描述:
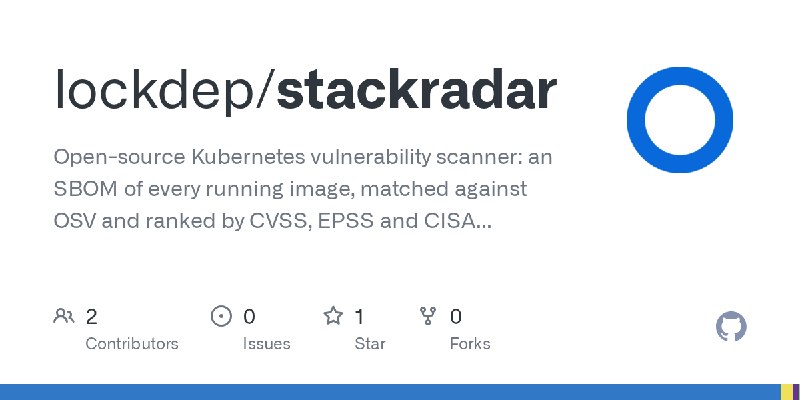
Open-source Kubernetes vulnerability scanner: an SBOM of every running image, matched against OSV and ranked by CVSS, EPSS and CISA KEV. Self-host with one Helm chart, or use the cloud.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #C2 #Framework
📦 项目名称: pullgoscript
👤 项目作者: DevCop95
🛠 开发语言: Go
⭐ Star数量: 20 | 🍴 Fork数量: 1
📅 更新时间: 2026-10-17 13:57:57
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #C2 #Framework
📦 项目名称: pullgoscript
👤 项目作者: DevCop95
🛠 开发语言: Go
⭐ Star数量: 20 | 🍴 Fork数量: 1
📅 更新时间: 2026-10-17 13:57:57
📝 项目描述:
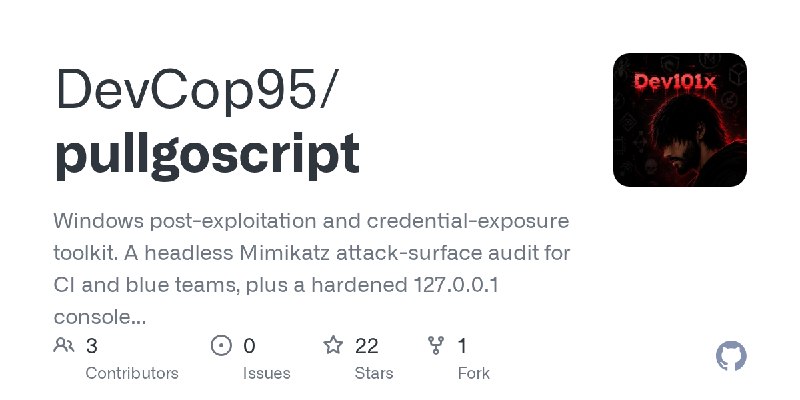
A lightweight Command & Control (C2) framework specialized for Windows environments, designed for Red Team operations and post-exploitation research.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Stored #Reflected
📦 项目名称: Web-Application-Security-Part-2
👤 项目作者: 10HUM
🛠 开发语言: Unknown
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 13:32:54
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Stored #Reflected
📦 项目名称: Web-Application-Security-Part-2
👤 项目作者: 10HUM
🛠 开发语言: Unknown
⭐ Star数量: 1 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 13:32:54
📝 项目描述:
A comprehensive web application penetration testing report and source code analysis evaluating Stored and Reflected XSS vulnerabilities across multiple security tiers using DVWA.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #Reflected
📦 项目名称: xss-vulnerability-tester
👤 项目作者: Nyashadzashe
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 13:25:42
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #Reflected
📦 项目名称: xss-vulnerability-tester
👤 项目作者: Nyashadzashe
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 13:25:42
📝 项目描述:
A Python Flask tool for testing potential reflected XSS vulnerabilities in authorised environments🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #SSTI #RCE
📦 项目名称: ssti-ctf-feedback-form
👤 项目作者: Pytech04
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 05:02:42
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #SSTI #RCE
📦 项目名称: ssti-ctf-feedback-form
👤 项目作者: Pytech04
🛠 开发语言: HTML
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 05:02:42
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #SSRF #metadata
📦 项目名称: dsh-reliable-web
👤 项目作者: dsh-plugin-db
🛠 开发语言: JavaScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 11:26:44
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #SSRF #metadata
📦 项目名称: dsh-reliable-web
👤 项目作者: dsh-plugin-db
🛠 开发语言: JavaScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 11:26:44
📝 项目描述:
Free, dependable web_search and web_fetch for DeepSeek Harness: fused keyless search plus optional Brave, SSRF-safe retrieval with reader escalation.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #SSRF #metadata
📦 项目名称: pre-ship-security-red-team
👤 项目作者: arm-pz
🛠 开发语言: JavaScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 13:04:51
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #SSRF #metadata
📦 项目名称: pre-ship-security-red-team
👤 项目作者: arm-pz
🛠 开发语言: JavaScript
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 13:04:51
📝 项目描述:
Agent skill that red-teams a web app you own before launch: three subagents run 14 authorization and abuse checks (IDOR, role escalation, quota races, open redirects, XSS, SSRF, cache leaks, prompt injection) with captured evidence, then fix and rerun. Local isolated environments only. Claude Code, Cursor, Qoder.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Exploit #CVE
📦 项目名称: CVE_2023_3460
👤 项目作者: ollie-blue
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:59:54
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Exploit #CVE
📦 项目名称: CVE_2023_3460
👤 项目作者: ollie-blue
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:59:54
📝 项目描述:
Exploit wp capabilities and wordPress ultimate member plugin to create admnistrator account🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: VulnWatch
👤 项目作者: Lucid1o
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:43:54
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: VulnWatch
👤 项目作者: Lucid1o
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:43:54
📝 项目描述:
A small vulnerability scanner and tracker for my own machines.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: Vuln-Guard-Web-Vulnerability-Scanner
👤 项目作者: khhadiya-09
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:59:27
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: Vuln-Guard-Web-Vulnerability-Scanner
👤 项目作者: khhadiya-09
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:59:27
📝 项目描述:
Python-based web vulnerability scanner with security header and cookie analysis, risk scoring, and a Streamlit dashboard.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #Exploit
📦 项目名称: cve-2026-64560-rmx6699
👤 项目作者: totsiaw
🛠 开发语言: C
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:56:32
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #Exploit
📦 项目名称: cve-2026-64560-rmx6699
👤 项目作者: totsiaw
🛠 开发语言: C
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:56:32
📝 项目描述:
CVE-2026-64560 temporary-root exploit for realme RMX6699 (Snapdragon 8 Elite, kernel 6.6.118, Android 17/COOS17)🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Exploit #CVE
📦 项目名称: VulnState
👤 项目作者: corifeo
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:01:35
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Exploit #CVE
📦 项目名称: VulnState
👤 项目作者: corifeo
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 12:01:35
📝 项目描述:
Model every CVE as a disclosure state machine: zero-day, coordination and fix-vs-exploit analytics over NVD, EPSS and CISA KEV data, vectorized with NumPy.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #CVE-2026 #利用
📦 项目名称: prague-CVE-2026-64560-OS4.0
👤 项目作者: ChaYeWuu
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 11:36:53
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #CVE-2026 #利用
📦 项目名称: prague-CVE-2026-64560-OS4.0
👤 项目作者: ChaYeWuu
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 11:36:53
📝 项目描述:
REDMI K90 Max在OS4.0.0.14.XAACNXM利用CVE-2026-64560获取ROOT权限。🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #C2 #Beacon
📦 项目名称: C2-Beacon-Detector
👤 项目作者: hab-git-1
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 11:02:47
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #C2 #Beacon
📦 项目名称: C2-Beacon-Detector
👤 项目作者: hab-git-1
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 11:02:47
📝 项目描述:
无描述🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #XSS #POC
📦 项目名称: wr-xss-proof
👤 项目作者: mahm0ud-ragab
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 10:26:42
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #XSS #POC
📦 项目名称: wr-xss-proof
👤 项目作者: mahm0ud-ragab
🛠 开发语言: Unknown
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 10:26:42
📝 项目描述:
TEMP: security PoC asset for authorized vulnerability report to WhatRuns (will be removed after triage)🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: Simple-Vulnerability-Scanner
👤 项目作者: Monisha569
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 09:43:32
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Vulnerability Scanner
📦 项目名称: Simple-Vulnerability-Scanner
👤 项目作者: Monisha569
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 0
📅 更新时间: 2026-10-17 09:43:32
📝 项目描述:
Sentinel is a Python-based vulnerability scanner that detects open ports, identifies software versions, checks HTTP security headers, performs basic CVE lookups using the NVD, and generates TXT and CSV scan reports.🔗 点击访问项目地址
🚨 GitHub 监控消息提醒
🚨 发现关键词: #Docker #Exploit
📦 项目名称: sentinel-matrix
👤 项目作者: kamisaberi
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 1
📅 更新时间: 2026-10-17 09:07:18
📝 项目描述:
🔗 点击访问项目地址
🚨 发现关键词: #Docker #Exploit
📦 项目名称: sentinel-matrix
👤 项目作者: kamisaberi
🛠 开发语言: Python
⭐ Star数量: 0 | 🍴 Fork数量: 1
📅 更新时间: 2026-10-17 09:07:18
📝 项目描述:
Encapsulated, autonomous cyber-range simulation mesh and multi-container digital twin for VMware and Docker environments.🔗 点击访问项目地址